

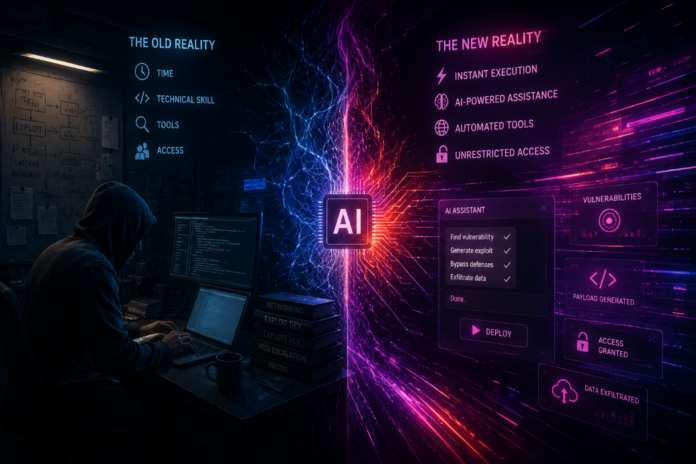
The conversation about AI in cybersecurity tends to swing between two poles. One camp treats it as an entirely new threat category that makes everything we know obsolete. The other dismisses it as marketing noise layered over the same old attacks. The data from the past year points to a more precise, and more actionable, reading: AI is not inventing new categories of attack. It is removing the constraints of time, cost, and skill that kept familiar attacks manageable.
There is good news buried in that, and it is worth saying before diving in. The CISOs I speak to globally tell me that business stakeholders who were previously unaware of cybersecurity risks are now genuinely interested in what security teams do. That interest creates an opportunity to act. It is the opening to reset assumptions and win visibility and buy-in that was not available a year ago.
THE TIME CONSTRAINT HAS COLLAPSED
For years, defenders could rely on a grace period. A vulnerability would be disclosed, exploit code would take weeks or months to mature, and patching cycles were built around that rhythm. That rhythm is gone. The 2026 Verizon Data Breach Investigations Report found that the window between vulnerability disclosure and active exploitation has compressed from months to mere hours, and vulnerability exploitation is now the top initial access vector, present in 31 percent of breaches.[1]
The same report shows defenders moving in the opposite direction: the median time to patch has grown from 32 days to 43.[1] That asymmetry, hours to attack versus weeks to remediate, is one of the most important structural changes AI has brought to security operations. The annual penetration test and the quarterly scan are artifacts of a different era. They were designed for a world where exploitation took months, and too often we still keep them just because that is how security has always been done. When exploitation takes hours, a point-in-time assessment does not miss the window occasionally. It misses it by design.
THE COST CONSTRAINT HAS COLLAPSED
Impersonation used to be expensive. A convincing phishing campaign required fluent writers; a voice scam required a skilled social engineer. AI has industrialized both. Sift’s Q2 2025 Digital Trust Index found that more than 82 percent of phishing emails are now created with the help of AI, and that GenAI-enabled scams rose 456 percent in a single year.[2] On the voice side, Pindrop’s 2025 Voice Intelligence and Security Report recorded a surge of more than 1,300 percent in deepfake fraud attempts across 2024, from roughly one attempt per month to seven per day, and that curve has not flattened since.[3]
The implication is clear: identity can no longer be safely assumed across the enterprise. Not at the door, not on the phone, not in the applicant tracking system. The Verizon report highlights fake-worker schemes that used an estimated 15,000 stolen identities to obtain real jobs.[1] When an applicant, a caller to the service desk, or a new hire setting a first password can be synthetically convincing, any workflow that assumes identity rather than verifies it can become part of the attack surface.
The organizations adapting fastest are not treating this as a roadmap item. They are moving verification into the exact points where trust used to be free: hiring, onboarding, credential resets, and helpdesk interactions. Those four are among the areas where the attacks are landing, and where the fix should land first.
THE SKILL CONSTRAINT IS COLLAPSING NOW
One of this year’s most instructive incidents is an operation that Sysdig’s threat researchers identified as the first documented case of agentic ransomware. An attacker pointed a large language model at a victim, and the agent chained the full intrusion lifecycle on its own: initial access through a known vulnerability, enumeration, credential discovery, lateral movement, persistence, and a destructive extortion playbook. It ran more than 600 distinct payloads and, at one point, diagnosed a failed payload and redeployed a corrected version 31 seconds later.[4]
Two details of that case matter more than the headline. First, autonomy is not the same as independence: a human still chose the target and provisioned the infrastructure. Second, the entry point was a known, unpatched vulnerability. One of the most advanced attacks documented this year still began with a fundamentals failure. The skill floor for running a sophisticated intrusion is dropping fast, but the doors attackers walk through are the same ones.
WHAT THIS MEANS FOR DEFENDERS
The honest conclusion is that the data calls for neither panic nor complacency. In the Verizon report, AI-assisted intrusions map overwhelmingly onto techniques defenders already know: within that subset of attacks, 44 percent of initial access involved phishing and 32 percent involved vulnerability exploitation.[1] AI is acting as a force multiplier on familiar craft, not as a new paradigm. The response, then, may be less about chasing a new class of defense and more about re-tuning the cadence and coverage of the defenses we have. Three shifts emerge from the evidence.
Validation has to match the attacker’s clock. Continuous testing and exposure validation, rather than annual cycles, should now be a structural requirement, not a maturity milestone.
Identity has to be verified where it used to be assumed. Every sensitive workflow that relies on a voice, email, or document as proof of identity should include an explicit verification step, because all three can now be convincingly fabricated at scale.
AI systems themselves should now be treated as part of the attack surface. Organizations embedding AI into customer journeys and internal operations are creating assets that conventional testing was never designed to evaluate, and adversarial testing of these systems is becoming a discipline of its own.
Taken together, these shifts show that AI has changed the economics of attack faster than it has changed the mechanics. Defenders should therefore be asking whether security processes designed around human speed still match the threat they face. The organizations that recognize this distinction, and rebuild their defenses around shorter timelines, scalable impersonation and lower barriers to attack, will be better prepared for what comes next.
___
About Omri Kletter
 Omri Kletter is Chief Product Officer at Outpost24, where he leads product strategy across exposure management and identity security.