While a single failed login rarely gets a second look from a security analyst, fifty failed logins across 20 accounts from one IP range in 10 minutes will. Security teams have worked this way for years, correlating logs rather than reading them line by line.
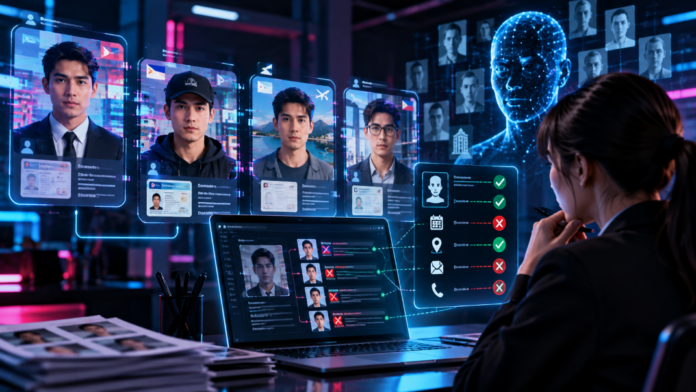
Onboarding checks still often evaluate one attribute at a time, which can miss coordinated fraud. Combining email, device, and address checks can build confidence in detection, reassuring security teams that verification is comprehensive.
A Passing Check Proves Less Than It Used To
Generative AI has made most pieces of an identity cheap to produce, including convincing deepfakes and synthetic identities. The Financial Action Task Force warns that anyone with a smartphone can generate convincing deepfakes in the time it takes to set up a social media profile, highlighting the need for detection strategies that address these sophisticated tactics.
Deepfakes go after document and selfie checks. Manufactured identities exploit the assumption that if each field on an application passes, the fields belong together. A manufactured application might have a valid email that shows up on none of the services a real inbox collects over the years, a phone number swapped to a new SIM or ported days ago, and an address in the same building as a dozen other new accounts opened this month. Each check passes on its own, yet together they point to an identity with no history before last week.
Where the Economics Break
Fraudsters can buy history. Aged and pre-verified accounts sell openly on account-trafficking sites. Patient operators season synthetic identities for months before busting out. Bought history rarely lines up across email, phone, device and address for every account a fraud ring runs. A real person’s email shows up across years of ordinary sign-ups, and they have usually had the same phone number for a long time. Building that record for hundreds of accounts at once is slow and expensive. It eats into the margin that the whole scheme depends on.
So fraud rings cut costs the way any business would, by reusing what they already have, and the reuse leaves marks. Supposedly unrelated accounts use the same building, cycling through unit numbers and spellings. An Android phone reports an eSIM that its claimed model doesn’t support. A device’s time zone, language and carrier network place it in one country while its IP address, a VPN exit, resolves to another. Any one of these can have an innocent explanation, but when several turn up on the same cluster of accounts, they often point to a shared operation.
What Connected Signals Expose
Multi-accounting is the clearest example. A bonus abuser opening 30 accounts can rotate names and emails, and anti-detect browsers will produce 30 different device fingerprints on request. The tools struggle to keep each fake device consistent, so a browser may claim a graphics card whose rendering output doesn’t match the device’s. Nor do they change the infrastructure underneath, so 30 brand-new profiles may still come through the same proxy pool and list the same building. Linked to what they share, the 30 accounts trace back to one operation.
Larger rings work the same way. In one recently published investigation, the same screen-brightness reading kept appearing across thousands of accounts, leading investigators to a ring operating on real Android phones. The reading proved little on its own, but it told the team where to look. Because the phones were real, checks built to catch emulators had nothing to flag.
Linking can also go wrong. Carrier-grade network address translation routes many unrelated users behind a single public IP address, and families share tablets. Good fraud teams give rare shared attributes more weight than common ones. They also have an analyst confirm a cluster before acting on it.
To combat smarter fraud, adding more steps, such as document uploads or challenge questions, can hinder legitimate customers. Instead, detection should focus on analyzing connected signals such as email, phone, device, and address consistency, which can improve fraud detection without compromising user experience.
Many connected signals are collected in the background, so they add no steps for the customer. A real applicant with years of consistent email, phone and device history gets through quickly because the evidence agrees with itself. Reviewers can spend their time on the accounts where it doesn’t. A thin footprint should prompt a closer look rather than a decline, since students, recent immigrants and those individuals who are careful about their privacy often have one, too.
The same logic applies after onboarding, where a session’s behavior should align with the customer’s history. A remote-access tool running during login can signal an account takeover. An active phone call during a payment, if the operating system detects it, can mean a scammer is coaching the customer through it. Catching either while the session is still open gives the team a chance to hold the payment before the money leaves.
Fraud teams should check whether an applicant’s attributes are consistent across all accounts, starting at sign-up. Each fake account then needs its own consistent history, and few rings can afford to build that hundreds of times over.
_____
About Husnain Bajwa
 Husnain Bajwa is a fraud and risk tech leader with 30+ years in cybersecurity, cloud platforms, and infrastructure. As SVP of Product – Risk Solutions at SEON, he leads innovation in fraud prevention and compliance. He previously held leadership roles at Beyond Identity, Hewlett Packard Enterprise, Aruba Networks, and Ericsson. Husnain is a recognized voice in risk management, championing data-driven, adaptive strategies to fight digital fraud and maintain compliance in a constantly evolving threat landscape.