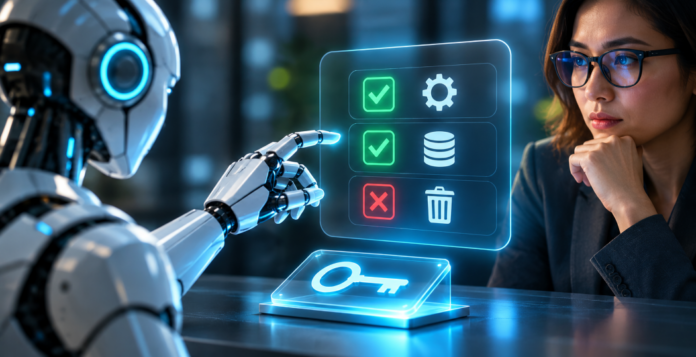
Autonomous machines are already moving through warehouses, hospitals, hotels and offices, carrying stock, delivering medication and patrolling after hours. Much of the security conversation around them has understandably focused on whether they can be hacked, and that matters. But there is a question that deserves just as much attention, and it comes first: what is each of these machines allowed to do, and who decided?
A robot is not a laptop with wheels. It has physical reach. It can move through a building, enter rooms, trigger doors and, increasingly, make its own decisions about where to go next. That makes it something our industry knows well, an identity with permissions, but one that behaves very differently from the identities we have managed before.
Consider a delivery robot in a hospital. To be useful, it needs the wards, the lifts and the supply rooms. Does it also need the pharmacy, the records office or the server room? In practice, a wide access profile is often the easiest way to get a deployment live, because narrowing it takes time and slows the rollout. Or consider a security robot on a night patrol, given access to areas no staff member could enter alone, precisely because it works when no one is watching. Each is a powerful standing credential held by a machine that may still be running on the same permissions years after the person who set it up has moved on.What makes this different from a badge is autonomy. A badge belongs to one person going to one place, and a human applies judgment at the door. A robot makes its own movement decisions, at machine speed, across the whole building. So “what is it allowed to do” can’t be a line in a spreadsheet set at installation. It needs to be a live question the system can answer at any moment, and revise when the robot’s job, location or condition changes.
There is also the connection home. These machines stay tethered to their manufacturers for updates, telemetry and remote support, which is entirely sensible. It is also another way into your building, one that never touches the badge reader. When the device on the other end can physically move and open things, a compromised update channel stops being only a data problem. It becomes a locked door that opens on its own.
The industry is rightly investing in making these machines safe. Nvidia describes its Halos platform as a full-stack safety system for physical AI, built to keep robots from colliding with or injuring people. That is functional safety, and it is essential. But it answers “will this machine hurt me,” not “should this machine be in this room.” A robot can be perfectly safe to stand next to and still have no business opening the door it just opened. Everyone is building the layer that stops the robot harming people. Almost no one is building the layer that governs what it is allowed to reach. That second layer is access control, and it is the one still missing.
None of this is an argument against physical AI. The productivity case is real, and these machines are coming. It is an argument for bringing them into our buildings thoughtfully, from the first unit rather than the thousandth. A handful of principles gets most of the way there:
- Start narrow. Give every machine the minimum access it needs to do its job, and make broad standing access the exception that needs sign-off, not the convenient default.
- Keep permissions live. The system should be able to say what a machine is allowed to do right now, and change the answer when its task, location or condition changes.
- Treat the manufacturer connection as an access path. Govern it as carefully as any other way into the building.
- Keep a record. Audit where each machine goes and what it opens, so there is something to learn from when something goes wrong.
- Build in clean revocation. When a unit is retired, sold or compromised, its authority should end the moment you decide, not whenever someone remembers.
Underneath all five sits one more: give every machine a named human owner. A permission no one owns is a permission no one reviews.
The reason to start now is simple arithmetic. The number of autonomous machines working in real buildings is still small, and the habits we set over the next couple of years will harden into the defaults for the next decade, just as they did with door controllers and networked cameras. If we onboard the first wave with broad access, no expiry and no audit trail, we won’t end up with a few badly governed robots. We will have written the problem into procurement and support contracts and made it expensive to unwind.
Done the other way, buildings become the place where physical AI earns its trust: every machine with a named owner, a clear purpose and access that expires. The technology is not the risk. The permissions are. We should decide what these machines are allowed to do before we hand them the keys, not after.
Join our LinkedIn group Information Security Community!