AI continues to become embedded in the modern workplace, especially as more employees seek innovative tools to work more efficiently and boost productivity. That demand can outpace the tools a business approves, encouraging shadow AI: the use of AI tools outside approved organizational controls and governance frameworks. That usage can result in organizations losing visibility into data usage and potential risks.
The Okta AI Agents at Work 2026 survey highlights a contrast between executive confidence and employee usage. Although 90% of surveyed executives are confident in their organizations’ visibility into AI tools, 52% of surveyed AI-using knowledge workers report having used AI tools without approval, often through personal accounts. Confidence in oversight is not the same as visibility into use.
The growing risk of shadow AI
The main issue with unauthorized AI usage is that it can too easily bypass governance that’s put in place. A lack of oversight directly contributes to a higher risk of errors, breaches, and sensitive data leakages. That exposure increases significantly should AI already be influencing business-critical activities, whether that be operational decision-making, software development, or content creation.
As companies move from AI that generates answers to agents that can take action, the risk depends increasingly on the permissions those agents receive. Without appropriate limits, mistakes can compound quickly. And if that AI system is operating outside approved frameworks, it could trigger harmful actions before intervention is possible. Of course, people remain accountable for outcomes, whatever the level of autonomy. Transparency and traceability will be critical to maintaining accountability, protecting ethical standards, and preserving the efficacy of AI systems as adoption continues to accelerate.
Building governance that works
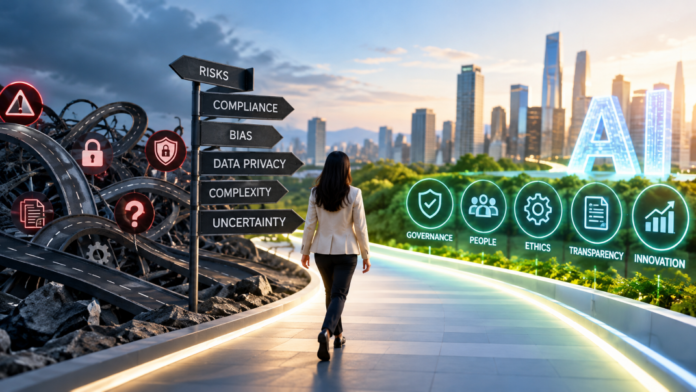
The best AI governance enables innovation, rather than stifling it. To achieve this, clear guardrails should be implemented that are integrated, transparent, auditable, and aligned with existing risk and compliance frameworks. For AI to be not only transformational, but safe, organizations must have the records to trace the data used, permissions granted and actions taken when issues arise.
Mature governance should begin with an approved AI tool stack that provides vetted options for the most common uses. This should be supported by risk-based policies that clarify what data is being used, sharing permissions, tool permissions, and what steps require human intervention or approval. Policies should also make clear which uses are permitted, which are prohibited, and which high-risk uses require approval. Data that’s confidential should be limited to enterprise tools which are approved and operating in accordance with regulations that apply in each jurisdiction. Put simply, governance needs to be customized to the risk of the use case. Summarizing public content carries different risks from summarizing a confidential contract or allowing an agent to change a customer record. This isn’t the place for one-size-fits-all policies.
Training can’t be overlooked either. Proper training isn’t just enforcing controls, but rather should include helping employees understand why those controls exist and how to use AI responsibly. As agents increasingly diagnose issues, recommend actions, and execute workflows with minimal input, oversight should focus on consequential actions and exceptions, with a named owner able to pause an agent or revoke access. Interoperability helps preserve consistent permissions and audit records across models and platforms, without requiring governance to be rebuilt for every new tool.
Putting responsible AI into practice
At its best, responsible AI adoption should be the path of least resistance. Employees often turn to shadow AI when approved tools and workflows are unavailable, difficult to access or fail to meet their needs. If shadow usage is surging, there’s a good chance that shadow tools are easier to access, faster to use or better suited to the task at hand. If the primary goal is cutting down shadow AI through means of restriction, that risks driving activity further underground and losing out on the efficiency and innovation gains that AI can deliver.
Once it’s understood that shadow AI use is often a symptom of unmet demand, leaders can focus their efforts on where AI is already being used across the business and ensure approved alternatives are available for the most common use cases. Building employees’ AI skills helps, but approved tools also need to be useful and easy to access. This is a critical part of building an AI-enabled culture, where tools, knowledge, and confidence work hand in hand.
Why trusted data is the foundation
An approved tool does not automatically produce a trustworthy answer. Without clear visibility into where data originates, who has accessed it, and whether it is current and fit for the task, even well-designed policies cannot keep AI in check. Agents operating on incomplete or ungoverned data can make poor decisions faster. Data quality, lineage, shared business definitions and access controls give people and agents a consistent basis for decisions.
Where to start
Progress does not require a multi-year program. Leaders can begin with three steps. First, establish what is already in use by surveying teams and reviewing usage data to understand which AI tools employees rely on and why. Second, prioritize security and legal review of the tools employees need most, and offer a suitable approved alternative where necessary. Third, set tiered rules that apply lighter guardrails to low-risk tasks and require stricter approvals for anything involving customer data or autonomous action.
What success looks like
For employees, the secure and approved path should also be the easiest one. When it is, the results are measurable: approved tool usage increases, shadow activity declines, new tools are approved faster. At the end of the day, more AI projects can move from pilot into production.
To show that governance is helping, leaders should track these speed and adoption gains alongside metrics like incident severity and unresolved audit findings. Growing adoption alongside effective risk controls suggests the framework is working. Should adoption stall or shadow usage increase, leaders should review tool usability and access as well as the guardrails.
Ultimately, strong governance and reliable, well-managed data give organizations the foundation to scale AI responsibly, reducing unnecessary risk without slowing progress.
Join our LinkedIn group Information Security Community!