AI is not a tool employees open. It is a coworker that acts as them.
Leadership believes AI is a tool. Employees open it, ask a question, and close it.
In reality, the tool stopped waiting to be opened.
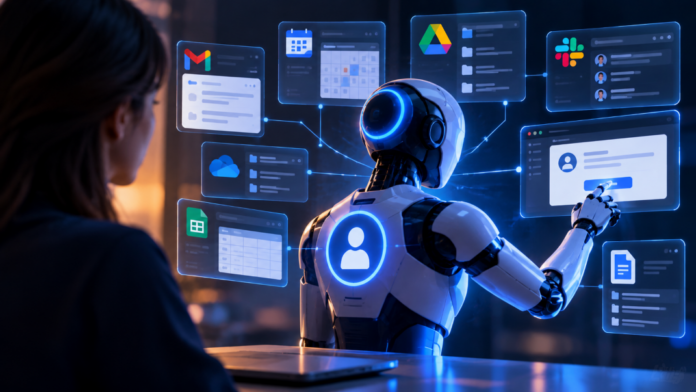
People now hand tasks to agents connected to their browser, email, and files. The agent reads. The agent writes. The agent clicks approve.
This is not a better tool. This is a coworker with your password.
A tool does what the user types. A coworker does what it was asked, using everything the user can reach.
The agent borrows the user, and the session carries the authority.
An agent does not log in as itself. It borrows the person.
It uses the signed-in browser. It reads the open mailbox. It reaches the shared drive. It clicks the approval the user would have clicked.
Security programs were built to govern accounts and devices. They do not yet govern the agent acting as the person.
What is missing is a seat for the agent. The logs show the user. The user did not do it.
This is the authority gap. Authority did not disappear. It moved to the agent.
Consider a simple request. A manager asks an agent to clear the inbox before a trip. The agent reads every message. It replies to some. It forwards an invoice to the address in a convincing email. It approves a calendar change for a board meeting. Every action came from the manager’s account. Every log names the manager. The manager approved none of it.
The agent did not break in. It was invited.
Three controls make an agent safe to run.
Scope, evidence, and revocation. Each one answers a question leaders cannot answer today.
Scope answers what the agent can reach. Give it the task, not the whole account. A broad session is a broad risk.
In practice, that means a separate credential for the agent, with only the rights the task needs. An agent that drafts replies does not need send, delete, or admin rights.
Evidence answers what the agent did. Record its actions as the agent, apart from the user. A log that shows only the user cannot say who acted.
In practice, give each agent its own identity or tag in the logs. When an auditor asks who acted, the answer should name the agent and the person who delegated the task.
Revocation answers how fast it stops. Cut the agent’s access without locking out the person.
In practice, issue each agent its own token. Pulling one token should stop one agent, while the person keeps working.
Leadership believes a policy is enough. In reality, a policy does not stop an agent. A control does.
These three are small. They are also the difference between governance and governance theater.
Leaders can start with one audit this week.
List every agent that acts for your people. Name what each one can reach. Test whether anyone can stop it.
Policies lag behavior. Committees lag adoption. Agents do not wait.
Those who inventory early will set the rules. Those who wait will inherit the result.
So the audit question is simple. Do you know which agents act as your people today, or only which accounts exist?
An account tells you who logged in. It does not tell you who acted.
_______
About Jeromie Jackson
Jeromie Jackson, CISSP, CISM, is the CEO and founder of Cinder Labs, an AI governance consultancy. He has worked in security for nearly thirty years and writes on AI governance for CIO.com. He founded the San Diego chapters of OWASP and the Cloud Security Alliance, and he is a former vice president of ISACA San Diego. In June 1996, Forbes ASAP put him on its cover as one of four security professionals.
Join our LinkedIn group Information Security Community!