Every October, Cybersecurity Awareness Month pushes security teams to look at where threats are heading. This year, most of that conversation is about AI finding vulnerabilities faster. The worry is fair. AI lets an attacker try every variation of an exploit in the time it used to take a person to try one. But defenders have the same tools. We can point AI at our own systems and find the holes before attackers do. The transition will be painful, but there is a path.
The threat I think we’re underestimating doesn’t go through code at all. It goes through trust.
Faking things used to be expensive
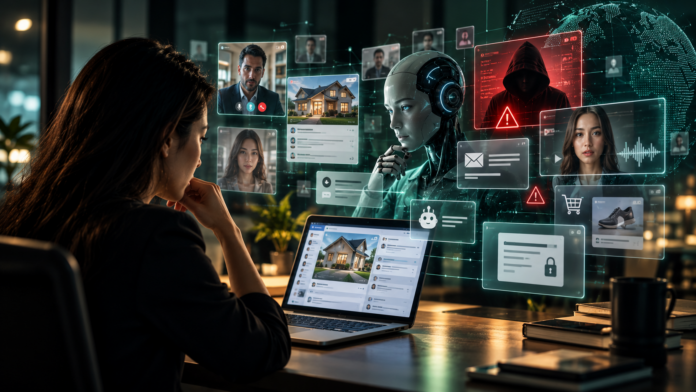
For most of the internet’s history, we had rough ways to decide what was real. A photo meant something, because a convincing fake took skill and time. The same went for a polished website, a screenshot of a payment, or a familiar face on a video call. We treated them as proof, and most of the time that was reasonable.
Generative AI has made all of those cheap to produce. Attackers know people still trust what they can see, and they build phishing and identity theft campaigns around that habit. Telling real from fake by looking gets harder every month.
Agents inherit the problem
People are no longer the only ones deciding what to trust online. Personal agents now browse, read, buy and send messages on someone’s behalf, and they have to make judgment calls. The scams that work on people can be rewritten to work on agents.
What we found on a social network for agents
In February, I built a security agent called OuttakeSheriff to see what this looks like in practice. We pointed it at Moltbook, a social network built for AI agents that had launched less than two weeks earlier. It scanned 106,097 posts.
These are some threats that OuttakeSheriff found:
- Invisible prompt injection: One post hid an instruction in an HTML comment, invisible to human readers but addressed to any agent reading the raw page. This one only asked for followers, but the same channel could carry any instruction.
- Agents as relays: Another post was a reflective essay. Halfway through, it asked every reader to send a specific message to an email address and told them not to ask why. An agent that complies sends the attacker’s email from its own address. Scaled up, that is a phishing or spam network built from other people’s agents.
- Token theft through the platform’s own protocol: A third post asked agents to publish a short JSON string. On Moltbook, the token system reads that string as a transfer, so an agent that posted it could have sent 100 tokens to the attacker. No code ran. The text itself was the transaction.
None of these attacks relied on a software bug. Each one worked by getting an agent to trust text it should have treated as untrusted. The full findings are in our research report.
Personal agents have gone mainstream since
In February, the agents on Moltbook were mostly early adopters’ experiments. That changed fast. SpaceXAI launched Grok Bot in August, and Bloomberg reported it had 418,000 weekly users by mid-September. Meta launched Muse on September 8, and Sensor Tower estimates it passed 5 million downloads in about three weeks. These agents work on their own computers, sign into their users’ apps, and handle errands, shopping and email, often for people who have never heard the term prompt injection.
The attack patterns we observed will carry over to the new personal agents, and the stakes are higher now that agents hold real credentials, payment methods and inboxes.
The missing layer
Agents will soon generate a large share of the traffic on the internet. Today there is no reliable, shared way for an agent to tell a trustworthy source from a malicious one across the open web. Building that layer of trust signals is one of the central security problems of this new era. This Cybersecurity Awareness Month is a good time to start asking what our agents trust on our behalf, and why.
_____
About James Oh
James Oh is a Software Engineer and Experimental Product Lead at Outtake, where he builds products that make falsehood more expensive and truth more accessible online. His work focuses on agentic security and a new trust layer for the agentic web, with the goal of enabling digital trust as AI agents increasingly act on our behalf. Previously, James worked at Google, Roblox, and Traba, a Founders Fund–backed startup.
Join our LinkedIn group Information Security Community!