
A severity label is useful context. It is not a complete explanation of what an analyst should investigate first. A short fictional exercise can expose that distinction without touching a production system or using a real person’s data.
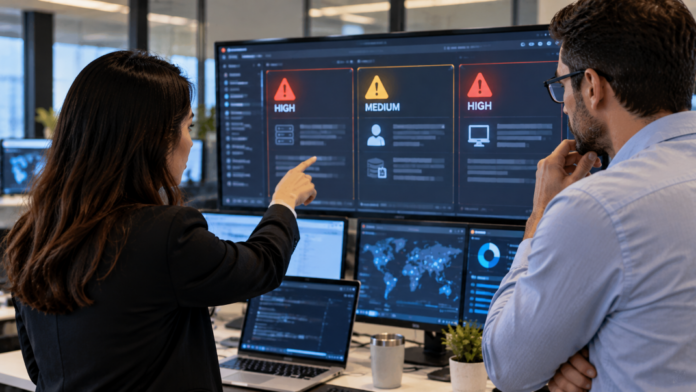
Imagine that one analyst has three alerts to review. Alert A is marked HIGH: 400 failed logins against a retired test service, with delayed success telemetry. Alert B is marked MEDIUM: a privileged payroll account signs in from a new device and then performs a bulk export; the account owner has not confirmed the activity. Alert C is marked HIGH: a scanner reports an administrative port on a training virtual machine, while the firewall record describes lab-only access.
Ask the learner to choose a first investigation and write down why. The objective is not to award points for guessing a hidden correct letter. It is to make the decision open to review.
Separate observation from conclusion
For each alert, record what is observed, what remains uncertain, the possible business impact, and the next check permitted by the exercise. Do not silently turn a label into evidence. Failed logins do not establish successful access. A bulk export does not establish theft. A scanner result does not establish that an administrative service is reachable from an untrusted network.
A defensible initial choice is B. Privileged access followed by a payroll export creates a plausible high-impact situation that deserves prompt verification. That is a reason to check the account owner’s context and authorized audit evidence, not proof of a breach. The learner should keep A and C open rather than treating lower priority as dismissal.
Make the decision note small enough to inspect
A useful note has four parts: the chosen alert, the evidence supporting the priority, the most important unknown, and the next authorized check. For B, the unknown might be whether the export was approved and expected. The next check should refer to the organization’s documented process and the analyst’s authority. The exercise must not teach learners to improvise access changes or disruptive containment.
Ask a second person to challenge the note. Which sentence is supported by the scenario? Which sentence is an inference? Could another analyst understand why this check comes before the other two? This review can happen in a classroom or learning discussion; it does not require an automated score.
Then change the facts
Now reveal that B was an approved export. For A, add a successful service-credential login and a previously missed trust relationship with production. Ask the learner to reorder the queue and explain the revision.
The value of the second round is the change in reasoning. Someone who chose B initially can still make a strong second decision by moving A higher when the evidence changes. Keeping the same answer to appear consistent is less useful than explaining what changed and why.
Keep the claim narrow
This exercise practices prioritization, uncertainty and a reviewable handoff. It does not establish that someone can operate a live security environment, validate a control or qualify for a job. Real investigations depend on the actual evidence, approved playbooks, escalation paths and decision authority.
The final question is simple: what additional fact would make you change your mind? An analyst who can answer it has made the limits of the current decision visible.
Optional related practice: https://ready-identity.com/training/google-cybersecurity/alert-prioritization-practice. A free READY account is required. Written work is self-reviewed in the learner’s own document; the resource does not save or grade it or award certification, course credit or READYScore.
About Ryan Corey
Ryan Corey represents READY, which develops independent career-training materials and career-development resources.
Editorial disclosure: Prepared with AI assistance and source checking. It has not received human cybersecurity-practitioner review; all scenario details are fictional.
Join our LinkedIn group Information Security Community!