
Insider Threat Awareness Month is an important reminder that some of the most difficult security threats to detect do not begin with an attacker breaking through the perimeter. They begin with activity that, at least initially, looks legitimate.
The term “insider threat” often brings to mind a malicious employee deliberately stealing sensitive information or sabotaging an organization. Those incidents happen, but they represent only one part of the problem. Insider risk can also stem from compromised credentials, negligent employees, contractors with legitimate access, former employees whose permissions have not been fully revoked, or trusted accounts behaving in ways they normally would not.
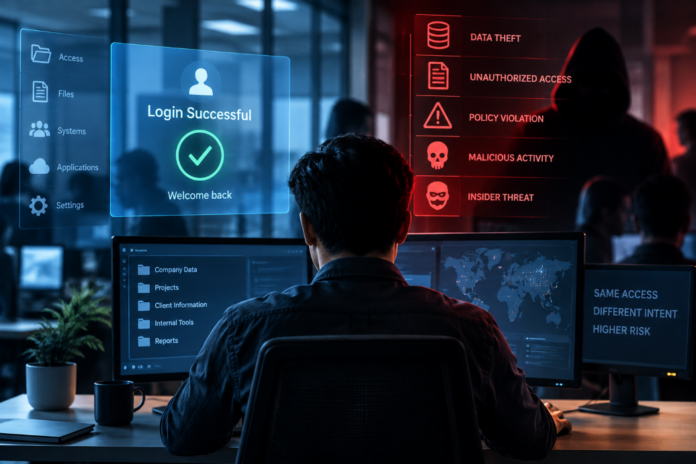
For CISOs, the distinction matters. An organization can authenticate a user correctly and still have no guarantee that what happens next is safe. Security teams need to move beyond simply asking, “Is this user authorized?” and increasingly ask, “Does this behavior make sense?”
Authentication establishes identity, not intent
Organizations have invested heavily in identity and access management, multifactor authentication and zero-trust architectures. Those controls remain essential, but none eliminates insider risk.
Consider an employee whose credentials have been compromised. The account is legitimate, and the permissions associated with it may be entirely appropriate. An attacker using those credentials can therefore operate inside the environment without immediately generating the signals associated with an obvious external intrusion.
The same challenge exists without a malicious attacker. An employee might download far more information than usual, access resources unrelated to their role, move sensitive files to an unauthorized location or use an unapproved application to complete a legitimate task.
Individually, those actions may not appear particularly alarming. Context is what makes them significant. Security teams consequently need visibility not only into who has access, but also into how that access is actually being used.
AI is expanding the definition of insider risk
Generative AI makes this challenge more complicated. Employees now have access to tools capable of analyzing documents, writing code, summarizing customer information and accelerating everyday work. The productivity benefits are significant, but so is the potential for sensitive information to move outside established security processes.
An employee does not need malicious intent to create an insider-risk event. Someone simply trying to work faster might paste proprietary source code, customer information, financial data or an internal document into an AI application without fully understanding where that information goes or how it may be retained.
That creates a form of insider risk that cannot be addressed through employee training alone or by attempting to block every new application. AI tools are evolving too quickly, and employees will continue searching for more efficient ways to work.
The challenge for security leaders is to create guardrails that enable innovation while preserving visibility into how users, applications and data are interacting.
Behavior can provide the warning
This is where behavioral visibility becomes increasingly important. Rather than treating every authenticated user as inherently trustworthy, security teams need to understand normal patterns of activity and recognize meaningful deviations.
One unusual event does not necessarily indicate malicious activity. Multiple signals viewed together, however, may tell a very different story.
An account might suddenly access systems it rarely uses. A device could begin communicating with infrastructure it has never contacted before. A user might generate an unusual volume of outbound traffic or connect to newly observed domains. None of those events automatically proves that an insider threat exists, but they provide valuable context for determining what deserves investigation.
Network and DNS activity can be particularly useful because they provide visibility into how users, devices, applications and workloads communicate. Unexpected connections, unusual query patterns, communications with newly registered or previously unseen domains, or traffic associated with attacker-controlled infrastructure can provide early indications that something has changed.
That visibility should complement identity and endpoint controls rather than replace them. Insider risk is rarely identified through a single signal. The objective is to connect enough context across the environment to recognize when otherwise legitimate activity begins to look abnormal.
Trust cannot be a permanent security state
The lesson for security leaders is not that organizations should distrust their employees. It is that trust cannot be treated as permanent.
A legitimate employee can make a mistake. A contractor’s credentials can be compromised. An authorized account can be hijacked. An employee can use an AI tool in a way that unintentionally exposes sensitive information. Throughout all of those events, the underlying identity may remain completely valid.
Organizations therefore need security controls capable of recognizing changes in behavior and giving teams enough context to investigate quickly. That means correlating identity, endpoint, network and DNS signals rather than treating successful authentication as the final determination of trust.
It also requires judgment. Security teams are already overwhelmed by alerts. Generating another alert whenever something unusual happens simply adds noise. The goal should be identifying deviations that matter and providing enough context to distinguish benign behavior from genuine risk.
Insider risk is ultimately a visibility problem
As organizations become more distributed and employees adopt more cloud, SaaS and AI tools, traditional boundaries around corporate information will continue to blur. Insider risk will become increasingly difficult to define by location, device or identity alone.
For CISOs, the more useful question is therefore shifting from “Who is inside?” to “What is happening once they are there?” Insider Threat Awareness Month is an opportunity to reconsider assumptions about what trusted activity looks like. Authentication remains critical, but a valid login is only the beginning of the security decision.
Understanding what happens after that login, across users, devices, applications, networks and data, gives security teams the opportunity to recognize when trusted activity begins behaving differently and intervene before unusual behavior becomes a larger security incident.
Join our LinkedIn group Information Security Community!