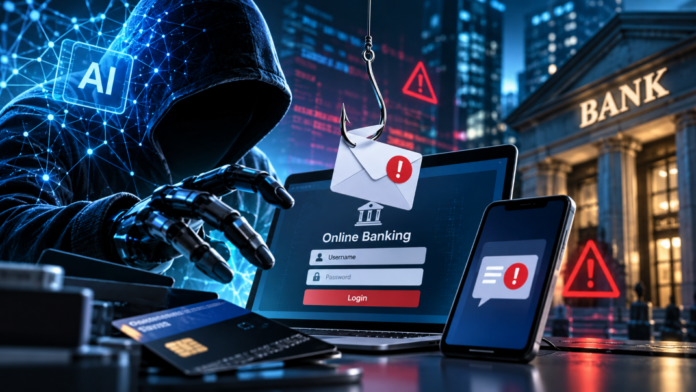
For years, we taught bank customers and employees to spot phishing by its flaws: clumsy grammar, an odd sender, a suspicious link. Those tells are vanishing. Fraudsters now have cheaper and better AI tools to create convincing messages, fake websites, cloned voices, and even deepfakes that make victims believe they are dealing with a trusted person or institution.
Scams are an age-old problem, but criminals have never been able to scale them this easily or this cheaply. In banking, where one successful scam can move money out the door in seconds, that changes everything.
The shift began in the inbox. Generative AI can draft thousands of variations of the same scam pitch, personalize each one, and keep refining what works. These attacks play on urgency, catching people when they are distracted. Dark web services like WormGPT and FraudGPT were just the start. Currently, defenders are struggling to keep up. In a recent survey, only eight percent of financial institutions said they were highly confident their employees could spot an AI-generated scam.
For banks, though, the threat has moved well beyond email. Today’s attacks are multichannel, blending text, voice and video in what’s known as 3D phishing. In a case made public this month, fraudsters sent the then-chairman of Italian private bank Fideuram a WhatsApp message that appeared to come from the CEO of its parent, Intesa Sanpaolo, then followed up with a call using an AI-cloned voice of a trusted lawyer. The bank wired about €95 million ($108 million) before spotting the irregularities, and roughly €36 million is still missing. Attackers are also going after the voice-recognition systems banks use to authenticate customers.
Malwarebytes’ findings demonstrate how effectively scammers can weaponize trust. AI lets fraudsters stand up polished, convincing fake websites in minutes and reuse them at scale. That matters enormously for payments fraud. When a customer is coached into authorizing a transfer, they pass every login and authentication check, because the person at the keyboard is genuine.
Catching these scams requires a different operating model: an adaptive, real-time AI decisioning layer that sees risk across the full customer journey instead of assessing a single event in isolation. The task is much more complex than verifying or flagging suspicious activity once. Banks must continuously monitor risk as it changes, connecting device, behavioral, account, transaction and network signals in real time. That broader view can uncover coordinated social-engineering campaigns and previously unseen fraud patterns—even when each individual interaction appears legitimate.
The objective is to intervene in real-time, before money has left the account. Doing that requires an intelligence layer that unifies signals across the customer journey, identifies both known and previously unseen fraud patterns, and turns that insight into thousands of precise decisions in a blink of an eye. This means stopping more fraud while removing unnecessary friction for legitimate customers.
There is no hiring our way out of this. Human analysts cannot keep pace with threats that mutate by the hour. AI-generated fraud is polymorphic: it can change its tactics, timing, language and behavior on the fly to evade static rules and controls. Defenders need AI that continuously learns from new signals, detects emerging patterns across channels and helps investigators focus on the cases where intervention will have the greatest impact.
The industry is moving from point-in-time identity verification to continuous trust. Banks should prioritize four steps:
- Take inventory. Understand how many siloed fraud and security tools are in use—and how much analyst time they consume. Fragmented signals mean slower, less confident decisions.
- Move beyond point-in-time checks. Treat identity as something to monitor continuously, not verify once.
- Connect the channels. Link email, mobile, web, call-center and payments data so a scam spanning several channels is seen as one event.
- Use the most advanced AI and agentic capabilities. Defenses should be proactive and adapt at machine speed, while being capable of handling thousands of decisions in milliseconds. That’s the time window for a bank to win or lose millions.
Banks should prepare for a continuous, faster and more adaptive fraud playbook rather than rely on static verification alone. Those that build real-time, adaptive defenses now will be better positioned to protect both their customers’ money and their trust.
Join our LinkedIn group Information Security Community!