

Serious cybercrime was once the work of skilled specialists, but it’s transformed into a highly accessible commodity.
The recently discovered stealer kit OnyxC2 is a striking example of this trend. It is so easy to acquire that accessing sophisticated cybercrime activities now feels less like a covert criminal undertaking and more like signing up for commercial software.
It’s stopped looking like malware in any traditional sense and has become a subscription business with a built-in support function, making it easier to launch attacks.
The priority now is how malware like OnyxC2 reaches your systems and what it can steal once it lands.
As-a-service economics are lowering the bar
Cybercrime is increasingly sold as a subscription, with the technical heavy lifting done once by a developer and then rented out indefinitely. Whatever the payload, the economics look the same: infrastructure, tooling and support bundled into a single price, available to anyone regardless of technical skill.
We’ve watched the influence of as-a-service kits in our own tracking of ransomware activity. The number of reported ransomware attacks has increased eightfold in just six years, and we identified at least 79 groups operating in the last year. Many of them are newcomers that wouldn’t have had the skills to launch these kinds of attacks just a few years ago.
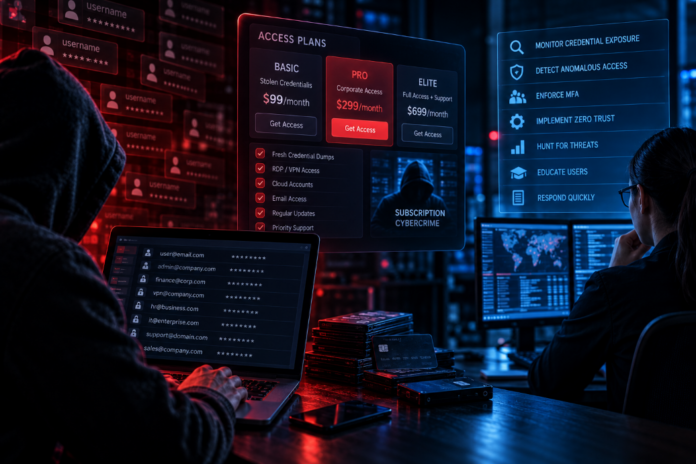
OnyxC2 shows the same economics applied to credential theft. A fee of $250 a month gets a build capable of targeting roughly 210 separate applications and extensions, covering browsers, password managers, two factor authentication tools and cryptocurrency wallets, with everything it collects routed back out through an encrypted channel. None of that requires the buyer to write a single line of code.
You simply log into an online dashboard, configure a build through a handful of settings, and choose from several pricing plans. It even comes with a money-back guarantee if it gets caught.
Inside the delivery chain
OnyxC2 is more than an appealing commercial package, and getting under the hood reveals engineering choices that make the stealer effective.
Investigating two live builds, we started picking them apart to see how they lined up with the seller’s spiel. Both showed up as password-protected archives, using ordinary-sounding names, Fling-Standalone, FinePrint, SystemSettings, and fake Windows update packages, to trick victims into opening them.
Sitting inside each archive is a sideloading pair, with the first being a legitimate, signed application that came back clean across all 71 antivirus engines. Alongside this sits a second file, a DLL crafted specifically to match the name and shape of a library the signed program already expects to find and load the moment it starts up. The victim only has to run what looks like a normal installer, and the trusted file does the rest of the work for the attacker.
Disguise runs right through to the DLL’s construction. Rather than looking suspicious, it’s built to resemble a NVIDIA graphics component and swollen out past 120MB, a size chosen because a number of scanning tools simply stop inspecting files once they cross a certain threshold. Buried inside that bulk, appended to code that is otherwise entirely legitimate, sits the real payload inside an encrypted section that is rebuilt with every new build.
Detonating the samples in a sandbox produced steady, repeated contact back to a single backend address, following the same structured routine every time. It registers the newly infected host, checks in periodically, retrieves configuration, and pushes stolen data back out.
What can defenders do about OnyxC2?
OnyxC2 isn’t so revolutionary that you need to overhaul your defenses with completely new tooling but dealing with it effectively does demand a shift in how threats are detected and dealt with. Installer provenance is the obvious starting point. A valid signature confirms the file itself hasn’t been altered, but it says nothing about what’s sitting in the same folder waiting to be loaded alongside it, so flagging signed applications that pull in DLLs from unexpected paths closes a gap that a clean signature alone will always miss.
Added to this, password managers and 2FA extensions deserve the same or arguably even more scrutiny as browsers and email clients, given that stealers like OnyxC2 target them by design. Treating the processes behind them as an afterthought leaves exactly the credentials attackers most want under the least amount of watching.
File size belongs in detection logic too. A file labeled as a graphics library but sitting north of 120MB should trigger a second look, since padding a payload past the size ceiling used by many scanners is a documented evasion technique.
The most important shift is treating exfiltration as the control point rather than an afterthought to intrusion detection. OnyxC2’s samples cleared antivirus scanning entirely on first submission, which rules out signature matching as a reliable line of defense on its own.
Watching for unusual outbound connections and unfamiliar check-in behavior helps, but the more reliable solution is blocking data from leaving the endpoint, regardless of which trusted process the transfer comes from or which domain it’s routed through.
Whatever slips past initial defenses, the attacker still needs stolen data to leave the building, and that is the one step in the chain reliably worth focusing on, whatever shape next month’s stealer happens to take.
The cybercrime market is changing, but the constants are the same
Stealers will keep getting easier to buy, and the target lists will keep growing. Chasing new malware kits and services feature by feature is a losing game.
What doesn’t change is the last step. Stolen passwords and hijacked sessions aren’t worth much if the attacker can’t get anything off the machine.
That is the thread running through OnyxC2 and the innumerable other -as-a-service offerings in the burgeoning underground economy.
The packaging gets slicker, the price gets lower and the barrier to entry keeps falling, but the payoff still depends on data making it out the door. Build your defense around stopping that one step, and it holds regardless of which subscription the attacker happened to sign up for.
Join our LinkedIn group Information Security Community!