It is the first Monday of December, the busiest stretch of the year for a neighborhood bakery taking holiday orders online. Sally opens her laptop to find three messages from regular customers, each asking the same thing: is your website safe? Their browsers are showing a full-page warning that the connection is not private. The site’s security certificate expired over the weekend, and the renewal reminder went to an email address belonging to Sally’s nephew, who built the site four years ago. By the time the certificate is reissued, a morning’s worth of orders has gone to the bakery across town, and some of those customers will never come back.
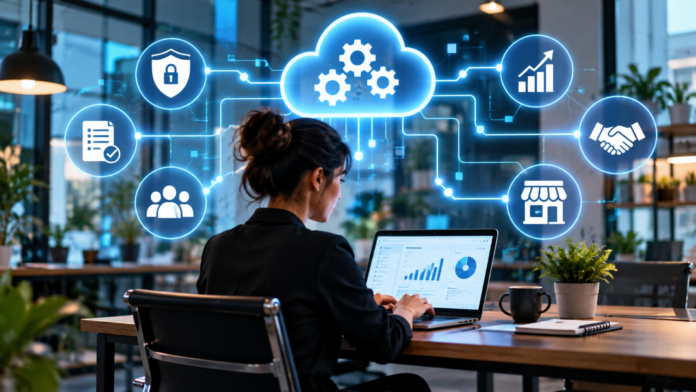
What happened to Sally is a small failure with a major cost, and it is about to become far more common. The certificates that encrypt websites and verify that a business is who it claims to be are being rebuilt from the ground up, on a schedule set by browser makers and certificate authorities with little input from the businesses that depend on them. In the AI era, trust is becoming one of the most important competitive advantages a business can have, and the infrastructure that earns it is shifting faster than any owner can track by hand.
Three simultaneous shifts
There are three shifts reshaping online trust at the same time, and each one raises the stakes of the others.
The first is the pace of renewal, which is accelerating on a fixed timetable. Under a schedule the CA/Browser Forum adopted in 2025, the maximum lifespan of a public SSL/TLS certificate fell from 398 days to 200 days this March, drops to 100 days in 2027, and reaches 47 days in 2029. At that point, every domain needs a new certificate roughly eight times a year. Large enterprises with dedicated teams already struggle to keep up: DigiCert’s latest Certificate Management Outlook found that more than a third of surveyed organizations experienced a service outage caused by an expired certificate in the past year, and every one of those organizations had more people watching its certificates than a bakery ever will.
The second is automation on both sides of every online interaction. AI is making attacks faster and cheaper to run at scale, and it is also changing who evaluates trust. Search engines, AI assistants, and automated agents now check certificate validity, domain health, and email authentication before deciding whether to surface a business or transact with it. A lapsed certificate reaches a customer as a warning page, and it reaches a machine as a reason to recommend someone else. AI amplifies whatever foundation already exists. Businesses with well-managed infrastructure see that amplification work in their favor, while those held together by calendar reminders and good intentions find every gap exposed at machine speed.
The third is the transition to post-quantum cryptography. NIST finalized its first quantum-resistant encryption standards in 2024 and has proposed retiring the algorithms most of today’s certificates rely on after 2030, with a full phase-out by 2035. With “harvest now, decrypt later” already on security teams’ planning horizon, the practical question for a small business is whether the provider managing its certificates is preparing for that change, because the owner has no realistic way to manage it alone.
Where the burden should go
Taken together, these shifts turn certificate management from an annual chore into a continuous discipline. That is a reasonable burden for an infrastructure provider running millions of domains, and an unreasonable one for Sally. According to the Guardz 2025 SMB Cybersecurity Report, 52% of small businesses rely on the owner or an untrained staff member to handle critical security functions, with no professional support. That gap extends well beyond the small businesses themselves, because they are the suppliers, agencies, and service partners larger organizations depend on, and a lapsed certificate or spoofed domain at a small vendor lands in enterprise inboxes and customer journeys all the same. Those owners are busy running a business, and they deserve protection that works in the background, built and maintained by people whose full-time job is getting it right.
That principle shaped a decision we made at Network Solutions recently, when we chose DigiCert as our certificate partner. The question behind it was simple: would the platform renew certificates automatically across millions of domains at 47-day lifecycles, and adapt to post-quantum standards as they arrive, without asking a single customer to change how they work? Every hosting provider will face that question over the next three years.
Key questions worth asking
Most small businesses turn to someone for technical help: an IT generalist, a managed service provider, a consultant, or a technically minded friend. Those advisors, and the owners themselves, should be putting three direct questions to every hosting provider. First, are certificate renewals fully automated, or does anything depend on a reminder email reaching the right person? Second, who is watching for failures, and how quickly are they fixed when something goes wrong? Third, what is the post-quantum migration plan, and when will it reach customer websites? A provider with clear answers has already taken on the complexity. A provider without them is quietly handing it back to the business owner and everyone who supports them.
Sally started her bakery to share a recipe she learned from her grandmother, and her website exists to bring customers to her door. Encryption standards, browser policy, and quantum timelines were never part of that plan, and keeping them off her plate is the job of the people who run the infrastructure she relies on. Trust is earned in that
infrastructure long before a customer places an order, and businesses whose certificates renew quietly in the background stay visible, stay recommended, and keep the customers who chose them. Protecting that trust automatically, through every renewal and every new standard, is work we take on so owners like Sally never have to think about it. That is the bar we are setting, and where our industry needs to go next.
______
About Sachin Puri
Sachin Puri is Chief Executive Officer of Bluehost Group and Network Solutions Group, leading a global, multi-brand digital platform ecosystem that helps millions of businesses establish identity and grow online.
Join our LinkedIn group Information Security Community!