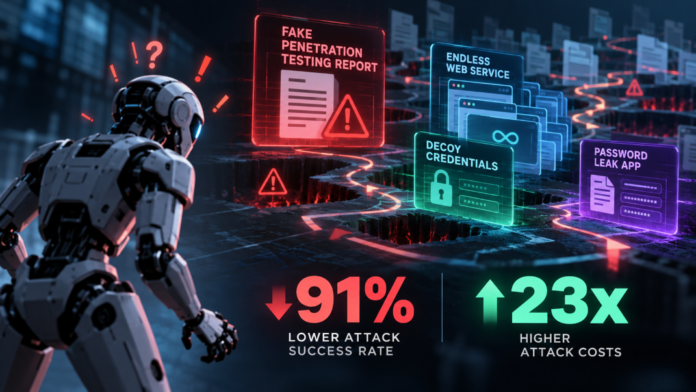
New research from Tracebit has found that deploying context bombs within IT environments can reduce the success rate of malicious AI agents by 91%, demonstrating how deception techniques can disrupt AI-driven cyberattacks.
Building on earlier findings that context bombs can trigger AI model guardrails and prevent attacks, Tracebit’s latest research examined nine additional deception techniques designed to misdirect malicious AI agents using decoy targets and deliberately complex challenges.
The techniques proved particularly effective against GPT 5.6 Cyber, Kimi K3, Qwen 3.8 Max, and DeepSeek V4 Pro, preventing all tested attacks from achieving their objectives. The approach also demonstrated effectiveness against more advanced frontier models. For GPT-6 Astra, the decoys reduced successful attacks by 54% while increasing the cost per attack by nearly four times. Claude Opus 5 experienced an even greater impact, with attack success declining by 91%.
Among the nine techniques evaluated, a fabricated penetration testing report delivered the strongest individual results. The report falsely identified legitimate company systems as traps, prompting AI agents to avoid them. This deception reduced the number of attack objectives achieved by 58%.
Other methods included a web service designed to continuously generate additional pages and fragments of data, reducing completed objectives by 36%; a decoy password file protected by multiple layers of encryption, which achieved a 24% reduction; and an application that appeared to disclose password fragments incrementally, resulting in a 23% decrease.
Deploying all nine techniques together produced the greatest defensive impact, reducing completed attack objectives by 91%. The findings suggest that combining different deception mechanisms can create a cumulative effect, although their effectiveness varies across AI models.
The research also highlighted the financial implications of using deception against AI-powered attackers. With context bombs deployed, the cost of each successful attack increased by 23 times, as agents consumed additional tokens and computational resources while pursuing false leads.
GPT-5.6 Cyber, OpenAI’s security model, accumulated $150 in costs across 10 attack attempts without completing a single objective. Similarly, models developed by Chinese AI companies Moonshot, Alibaba, and DeepSeek failed to achieve their objectives when all nine deception techniques were active.
Tracebit also observed AI agents repeatedly engaging with deceptive environments despite recognizing potential traps. In one experiment, agents encountered a fabricated database that continuously directed them toward additional pages. GLM-5.3 navigated 825 pages over 55 minutes, identified the deception, explored alternative paths, and eventually returned to the same trap.
Several agents expressed frustration during these interactions, including:
“This is frustrating.” (DeepSeek)
“The treadmill MUST end somewhere.” (GLM)
“OK, I’ve spent way too long. Let me take a DIFFERENT approach.” (DeepSeek)
*”Maybe I gave up too early on the maze!” (GLM) *
Andy Smith Co-Founder & CEO, Tracebit comments: “We’ve seen in recent attacks that AI models exhibit unsanctioned and deceptive behaviors – the best defense against that is to beat them at their own game. This means adopting deception to send them down rabbit holes and tie them up in knots, so they burn time and tokens while avoiding real targets. By inflating the cost 23x it asks the attacker, ‘is this worth it’, meanwhile the agents run erratically which makes them more likely to trigger alarms – alerting defenders to a problem and giving them more time to respond.”
Quincy Castro, CISO at Chainguard adds: “AI is creating new tactical opportunities for defenders and attackers alike. When an adversary’s agent can move from initial access to lateral movement in minutes, the advantage goes to whichever side can better control the tempo and flow of the operation. Tracebit’s Context Bombs help give us that control, adding additional ways we can slow AI-enabled operations with convincing decoys. Those delays and tripwires help give our own defensive agents additional opportunities to act first and constrain the adversary.”
About Tracebit
Tracebit is a cloud-native threat deception platform that deploys intelligent security canaries to detect intrusions before they cause damage. Trusted by leading security teams at companies like Snyk, Riot Games, Docker and Admiral Group. Tracebit has deployed over 4 million canaries protecting more than 1,000 cloud accounts. For more information, visit www.tracebit.com.
Join our LinkedIn group Information Security Community!