Insider threat has been in the news quite a bit lately, and one of the loudest examples is the recent OpenAI engineer case. On October 13, the Department of Justice announced charges against an OpenAI engineer accused of hiding an audio recording device in an executive conference room at the company’s San Francisco office. According to the complaint, the room hosted discussions of confidential technical, commercial and strategic information. Federal officials described the case as a matter of national security, not only a corporate one.
OpenAI staff moved swiftly after finding the device, leading to an equally swift FBI arrest a mere 9 days after discovery. The company used its own models to understand what it was and trace where it came from, which led to a specific employee. Before AI, that attribution would likely have taken significantly longer, if it happened at all.
Cases like this show why identifying insider threats before an incident occurs is so important. The device wasn’t the beginning of the threat, in fact it’s much more endgame than opening. Everything that happened before anyone found it is what warrants more study: weeks of quieter activity that pointed in the same direction once you read it together.
Discovery is the boom
In insider incidents, discovery is usually the boom. In this case, it was a physical device, but this can also be digital, like a file appearing somewhere it shouldn’t. The problem there is that by the time of discovery, the work is forensic, and forensics are reactive. You are reconstructing what happened, not changing what happens next.
This is exactly why we harp on proactive risk management. The criminal complaint describes a sequence that started well before the device was found, and much of it happened in software the company already ran.
The timeline
Figure 1 shows the multiple preemptive touch points plainly. The first event showed up in July and ran all the way until the arrest in October. (It’s important to note that all of the following are allegations from the complaint and the DOJ release, not proven findings.)
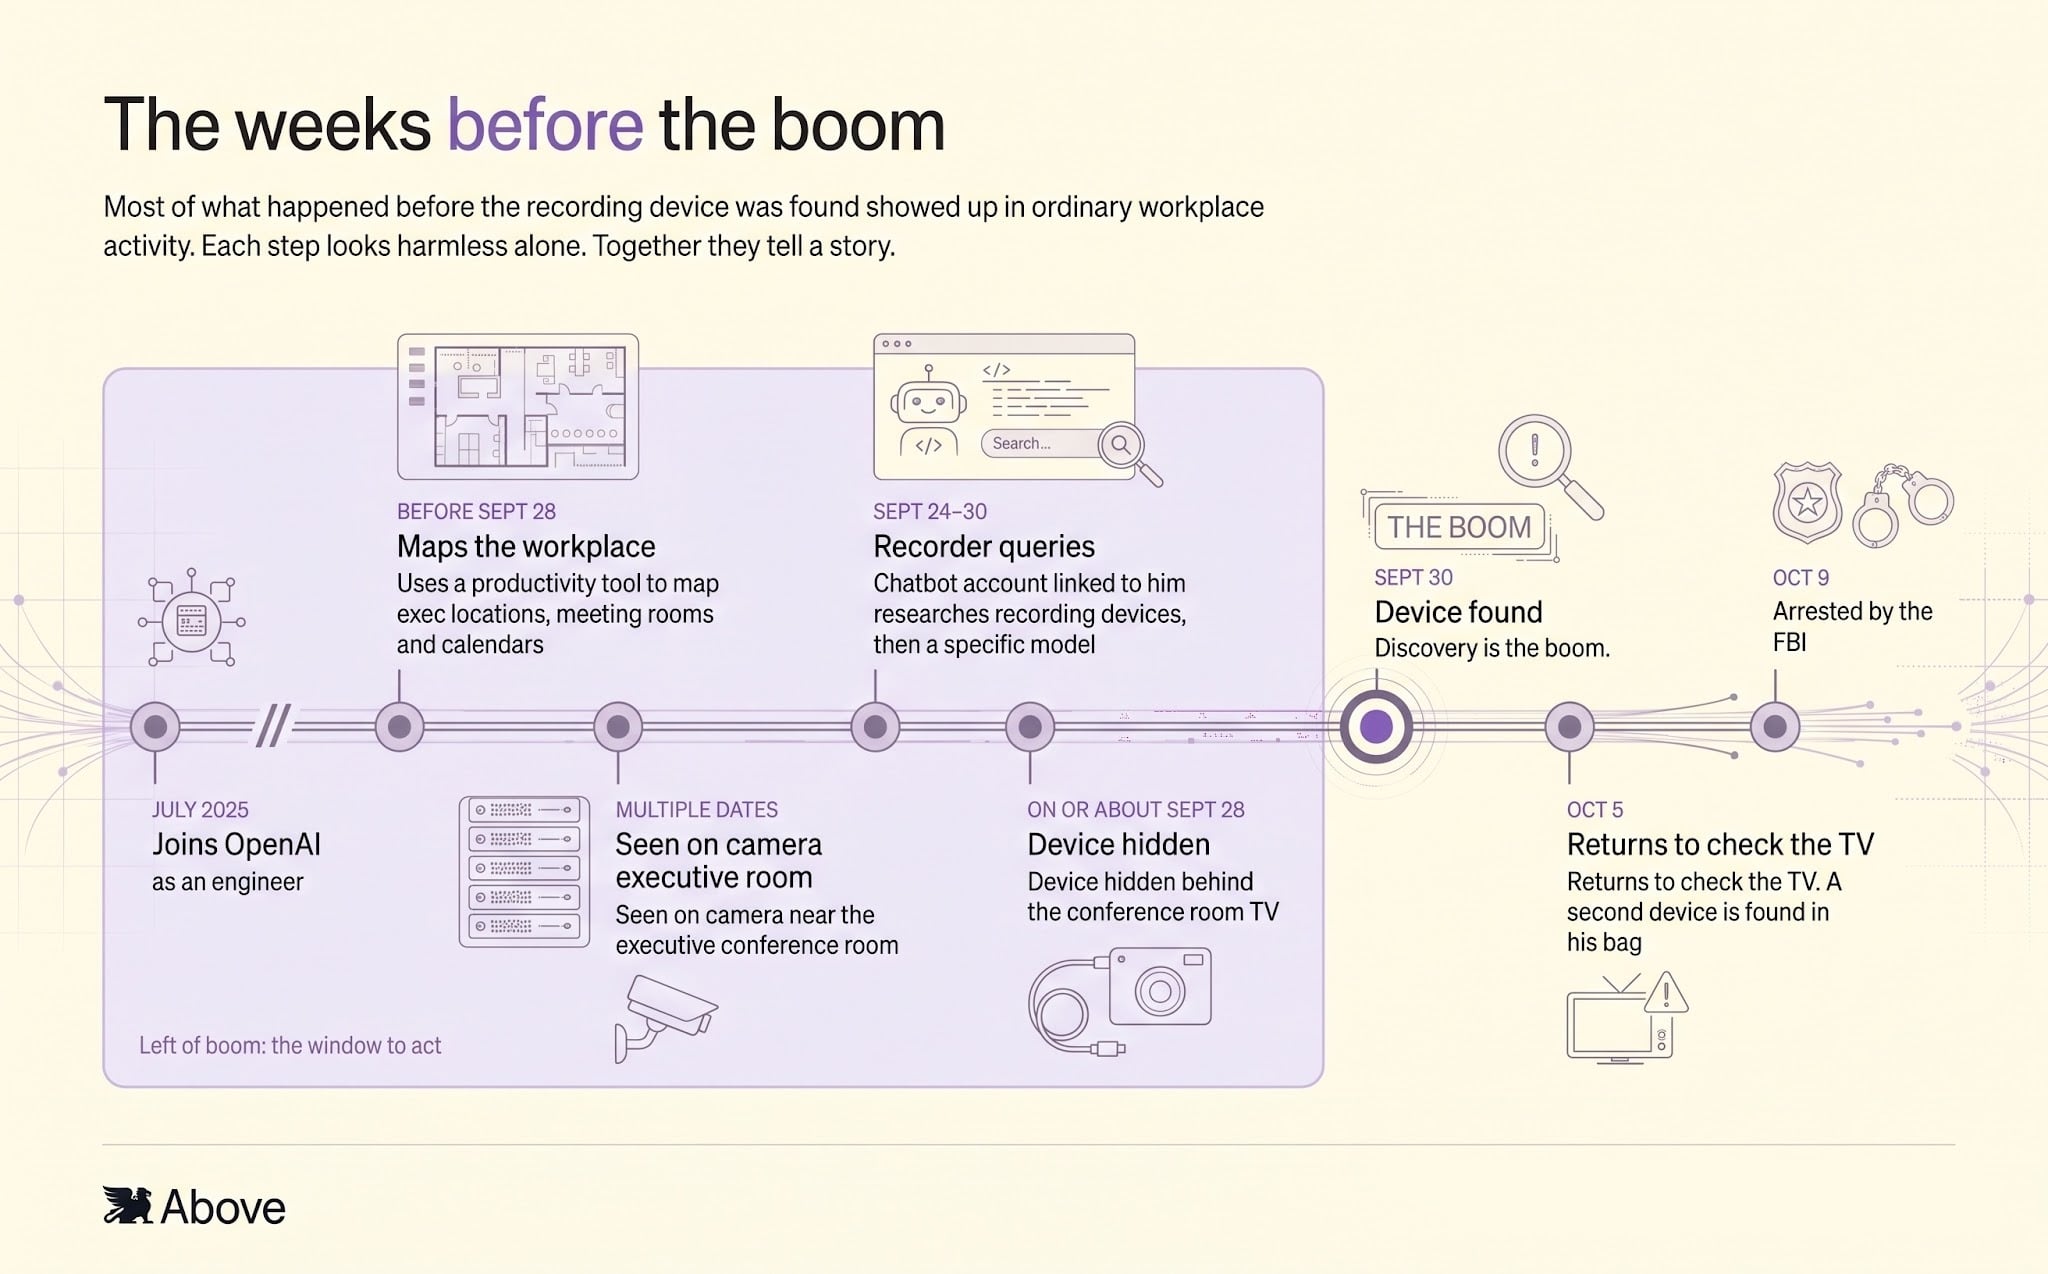
Fig. 1: Timeline of alleged misconduct
Lay that out and a familiar shape appears: reconnaissance, planning, acquisition, execution. Notice where finding the physical device sits on the timeline: the very end. The reconnaissance is what sits at the very beginning, and it was digital.
Individually innocent, collectively loud
Insider risk, especially modern and sophisticated insider risk, is treacherous because it lives in very legitimate, everyday workflows. Every early signal on that list has an innocent explanation. Engineers book meeting rooms all day. Asking where leadership sits could mean someone wants a hallway conversation with the CTO. Walking past a conference room is not a policy violation.
That is exactly why traditional tooling stays quiet here. No data moved, so a DLP policy has nothing to fire on. No single event crosses a threshold, so a rules engine shrugs. An anomaly score might twitch, then get tuned away as noise because deviation on its own is not risk.
What changes the picture is the combination, read in context. An engineer with no role in executive meetings, mapping where executives sit and when they meet, then lingering near the room where those meetings happen. The useful question is not “is this event unusual?” It is “why is this person doing this, right now?” and “What else have they done that could be a contributing factor?”
That is what moves from anomaly detection to actual risk management. Deviation doesn’t inherently mean risk, but multiple deviations can certainly mean risk.
What left of boom looks like in practice
Organizations often ask what they can do to identify insider threats earlier, before an incident occurs. Here are a few practical steps worth considering:
Treat reconnaissance as a signal. Most programs are built to catch the exfiltration event. The higher-value window is earlier, when someone is learning the environment and planning. AI-driven behavioral investigations can help identify early signs of reconnaissance and planning, examining how different activities relate to one another before any data moves.
Bring the human context in. “Searched for executive calendars” means nothing without “who is this person, what is their role, and has anything changed?” Combining technical activity with organizational context, including an employee’s role, department, manager and tenure, helps investigators distinguish expected behavior from activity that warrants a closer look.
Connect the threads into one story. In this case the threads ran across a productivity tool, a chatbot account and camera footage. Bringing relevant evidence together in a time-ordered timeline helps security teams understand how events are connected and why certain behavior may be concerning, rather than reviewing each alert in isolation.
Escalate attention, not accusations. Early signals justify a closer look, not a conclusion. Teams can place an identity on a watch list so investigators prioritize that person’s activity, with Security, HR and Legal each seeing what their role allows.
Be honest about the edges. Some of the signals in this case would not, and should not, show up in any workplace monitoring tool. A chatbot account belonging to a spouse sits outside the employer’s world. Digital security monitoring also has its limits. Physical activity captured by badge readers or camera footage may need to be reviewed separately from digital telemetry. Strong programs pair behavioral investigation with physical security and HR, and they draw clear lines around what is in scope.
Don’t wait for the boom
Most insider risk tools were built to wait. They wait for a file to move, a policy to break or a threshold to trip, then they hand a security team an alert and a reconstruction job. That works fine when the risk shows up as a single loud event. It works poorly when the risk looks like this case: weeks of quiet, ordinary-looking activity that only means something once someone connects it.
A more proactive approach focuses on investigating behavior as it happens, rather than relying solely on predefined rules. AI-driven investigators can examine activity across identities, SaaS applications, data and endpoints, asking the same questions an experienced security analyst would: who is this person, what is normal for them, what changed, and why now? When something warrants attention, analysts should have access to a clear timeline and the reasoning behind it, rather than another isolated alert to investigate.
Insider risk is an investigation problem, not a policy problem. It’s also a timing problem. The earlier you can read the pattern, the more options you have, and the more likely the outcome is a conversation instead of an arrest.
The challenge is recognizing when risk starts developing, rather than waiting until someone finds the recording device.
Join our LinkedIn group Information Security Community!